GlassHouse Systems Named A Great Place To Work!Read more
iTL:DR
GHS PODCASTS
Episode 01: Risk Management Over Tools
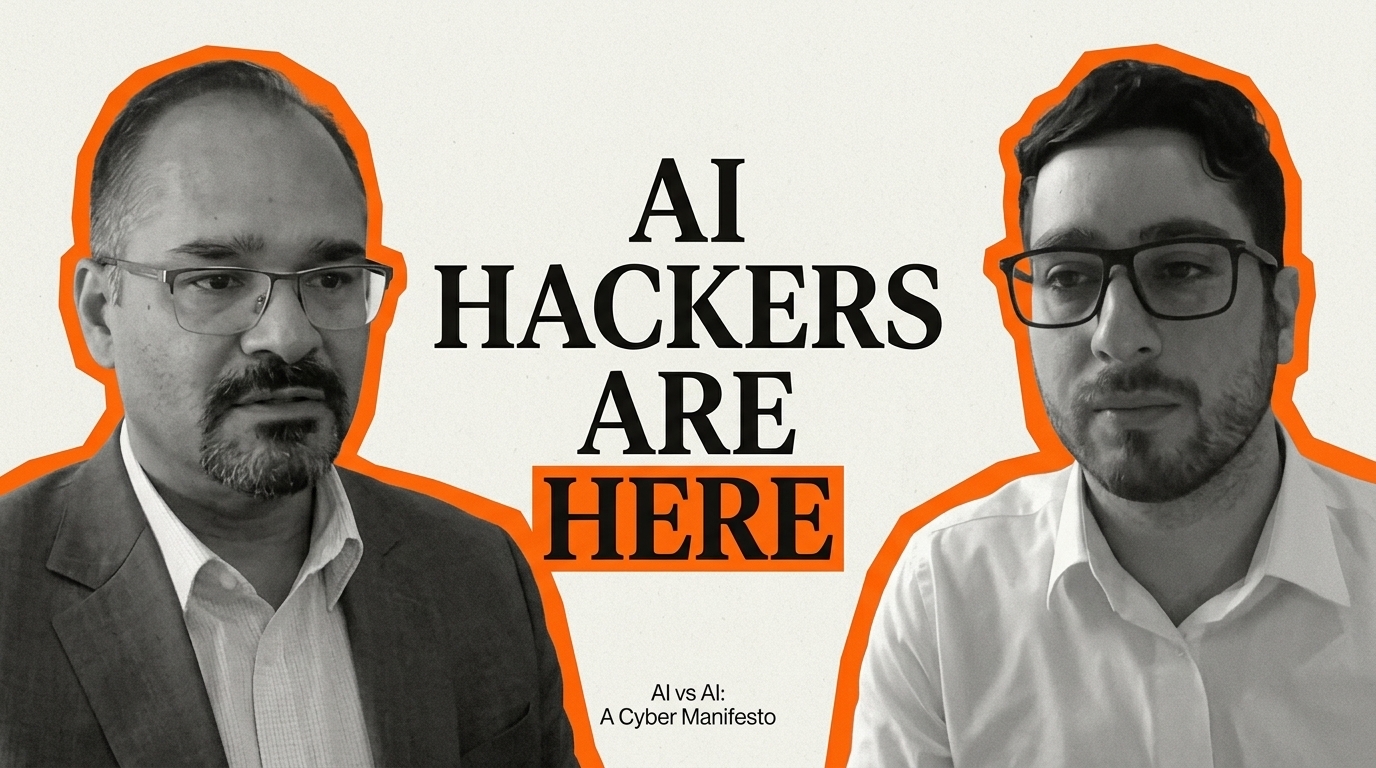
Guest: Snehal Antani, Founder & CEO, Horizon3.ai
Episode Overview
AI hackers are already outrunning traditional defenses, and Snehal Antani says most security teams are still looking at the problem the wrong way. If you care about cyber resilience, EDR, identity controls, and what actually stops an attacker in 76 seconds or less, this conversation will change how you think about defense.
Snehal, CEO and founder of Horizon3, breaks down why the future of cyber is AI versus AI with humans by exception—and why the most dangerous assumption in security is that buying the tool means you are protected. He explains how Horizon3’s autonomous pen testing uncovered shocking misconfigurations, including enterprise EDR deployments that only stopped an implant 16% to 31% of the time, and why a single bad configuration can be all it takes for an attacker to move from code execution to domain admin.
You'll discover:
Why the attacker’s perspective is the only one that matters for prioritizing risk
How Snehal uses a 3-part framework to decide what to fix first: exploitable, weaponized by threat actors, and business-critical
Why deception and honey tokens may be the cheapest, fastest way to stop agentic attackers
The third defensive pillar he says matters most after perimeter controls and EDR
Why vulnerability management tools are being replaced by attack path analysis, not more CVE lists
Snehal also shares the career arc that led him from IBM, GE Capital, Splunk, and JSOC to founding a multi-unicorn cyber company, and why each stop gave him a different “Lego block” for leadership, product, scale, and crisis management. Along the way, he explains why AI changes the economics of targeting, why the long tail of businesses is now exposed, and why compliance and resilience are very different things.
If you want a sharper view of how modern attackers operate—and what security leaders need to do before the next breach makes the news—this episode is essential listening.
How can we help?
Feel free to ask a question or simply leave a comment